Capabilities and services
NOETIX works across three pillars, supported by named executive services, specialist delivery partners and our own NoetixGRC platform.
Senior leadership you can retain.
Three named ways to bring senior security, privacy and governance leadership into your organisation without building the function from scratch first. Each is senior led and supported by technology we build ourselves.
Virtual CISO
A named senior security leader for security strategy, operating model design, cyber risk, resilience, assurance, board and regulator reporting and security programme leadership, on a fractional or retained basis.
Explore the vCISO mandateVirtual DPO and Privacy Advisory
Privacy governance and DPO oversight covering GDPR accountability, DPIAs, ROPA, processor and third party privacy governance, breach support and regulator facing readiness. Advisory and governance support, not legal representation.
Explore privacy leadershipExecutive and Board Advisory
Decision support for boards and C-suite on digital risk appetite, regulatory strategy, resilience, transformation and governance structure, so accountability sits where it belongs.
Discuss your governance prioritiesSix service lines, one accountable owner.
Advisory and leadership are delivered by NOETIX. Technical execution is either enabled by our own tooling or delivered with vetted specialist partners, and we are explicit about which is which.
Cybersecurity and Digital Risk Advisory
Security strategy, cyber risk and security governance for organisations that need to know where they are genuinely exposed, what to fix first, and how to hold the improvement in place.
Virtual CISO
Fractional or retained CISO leadership: a named senior owner for your security roadmap, governance, board reporting and programme oversight, without building the full function first.
Governance, Risk and Compliance
One control set that answers to your board, your auditors and your regulators, covering ISO 27001, DORA, NIS2, PCI DSS, ICT risk and third party risk rather than running them as competing programmes.
AI Governance and Security
An AI governance operating model that lets the organisation adopt artificial intelligence deliberately, with EU AI Act readiness, risk assessment and controls over models, data and agentic systems.
Privacy and Virtual DPO
Privacy governance with a named senior owner: GDPR accountability, DPIAs, ROPA, processor oversight and regulator facing readiness, delivered as advisory and governance support rather than legal representation.
Digital Assets and Crypto Risk
Security, resilience and governance for digital asset and crypto environments, where custody, key management and supervisory expectations move faster than most control frameworks.
NoetixGRC Platform
NoetixGRC is technology built by NOETIX, not a service in itself. It accelerates our advisory and governance work with 23 integrated modules, so evidence, controls and reporting stay current between engagements.
Dashboard
Centralised view of your entire security posture in real time, with key risk indicators, compliance status, and actionable alerts at a glance.
Internal Audit
Plan, execute, and track internal audits with structured workflows, evidence collection, and automated finding management.
Incident Response
Automated incident detection and response workflows with escalation rules, root cause tracking, and post-incident reporting.
Data Privacy
End-to-end GDPR, CCPA, and POPIA compliance management including consent tracking, DPIA workflows, and breach notification.
Policy Library
Centralised repository for all governance policies with version control, approval workflows, and employee attestation tracking.
Risk Assessment
Quantify and score cyber risks across your organisation using industry frameworks, heat maps, and scenario-based analysis.
Risk Register
Maintain a dynamic register of identified risks with ownership assignment, mitigation plans, and status monitoring in real time.
Third-Party Risk
Assess and continuously monitor vendor security posture with automated questionnaires, scoring, and SLA compliance tracking.
Compliance Controls
Map regulatory requirements to internal controls, monitor implementation status, and generate compliance evidence automatically.
Regulatory Analysis
Perform gap analysis against ICT regulations like DORA, NIS2, and ISO 27001 with actionable remediation roadmaps.
Asset Management
Discover, classify, and track all IT assets including hardware, software, cloud services, and their associated risk profiles.
Vulnerabilities
Centralise vulnerability findings from scanners, prioritise by business impact, and track remediation through to resolution.
Reports & Analytics
Generate reports ready for the board and drill-down analytics on risk trends, compliance metrics, and operational performance.
Tasks
Assign, track, and manage compliance and remediation tasks with deadlines, dependencies, and automated reminders.
Document Repository
Securely store and organise audit evidence, policies, and compliance artefacts with full version history and access controls.
Whistleblowing
Provide an anonymous, secure reporting channel for employees to raise concerns with built-in case management workflows.
Integrations
Connect NoetixGRC with your existing tech stack, including SIEM, ITSM, cloud providers, and identity platforms, via ready-made connectors.
Team Settings
Manage users, roles, and permissions with granular access controls, SSO integration, and organisational hierarchy mapping.
Executive Dashboard
Strategic-level metrics and KRIs designed for board members and C-suite, with trend analysis and benchmarking insights.
Documentation
Comprehensive help centre with guides, API documentation, best practices, and onboarding resources for all user roles.
Workflows
Design and automate GRC processes with a visual workflow builder, handling approvals, escalations, and notifications.
Audit Log
Activity records capturing every user action for accountability and regulatory audit trails.
Access Control
Fine-grained access controls, based on roles and attributes, ensuring least-privilege access across the entire platform.
Clear oversight. Connected governance.
Executive reporting, security operations and programme oversight, with a shared view of risk, control implementation and performance against targets.
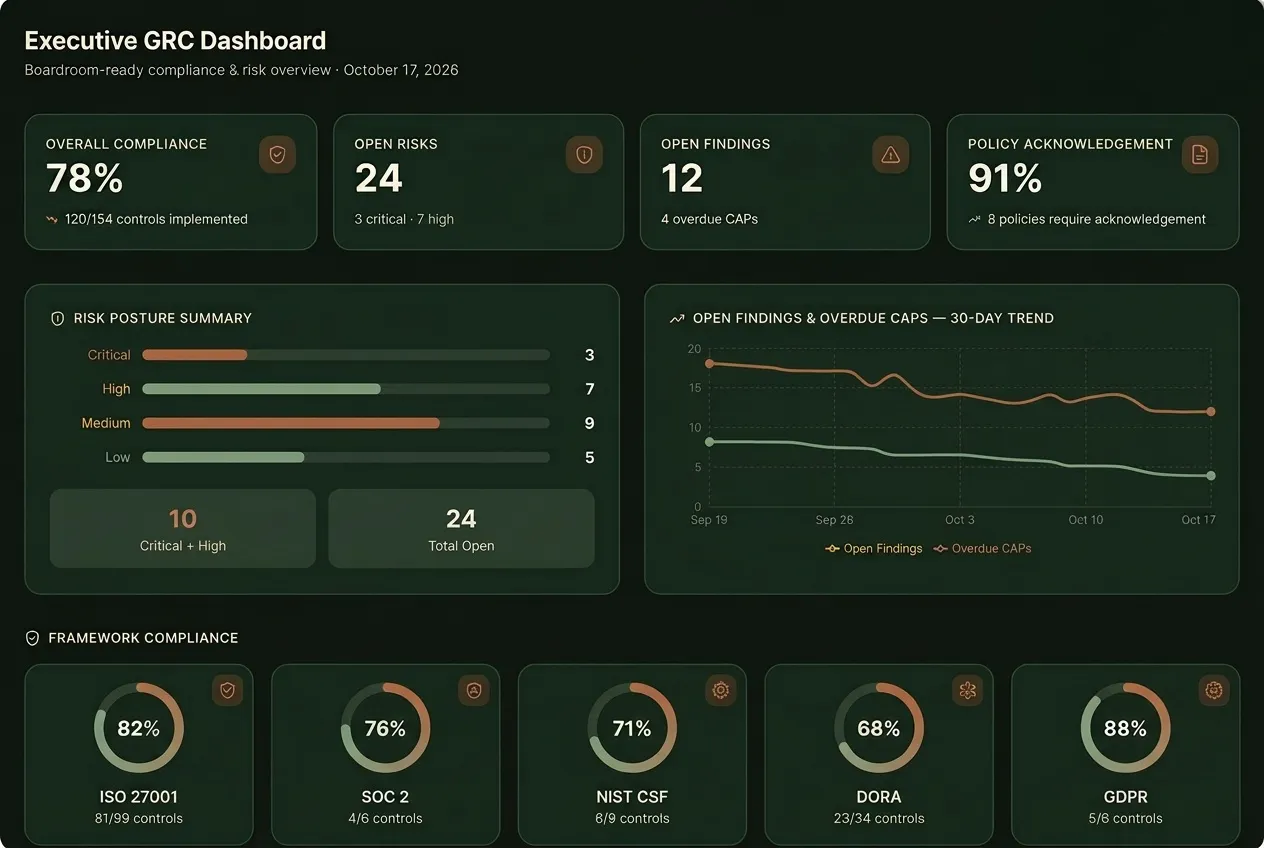
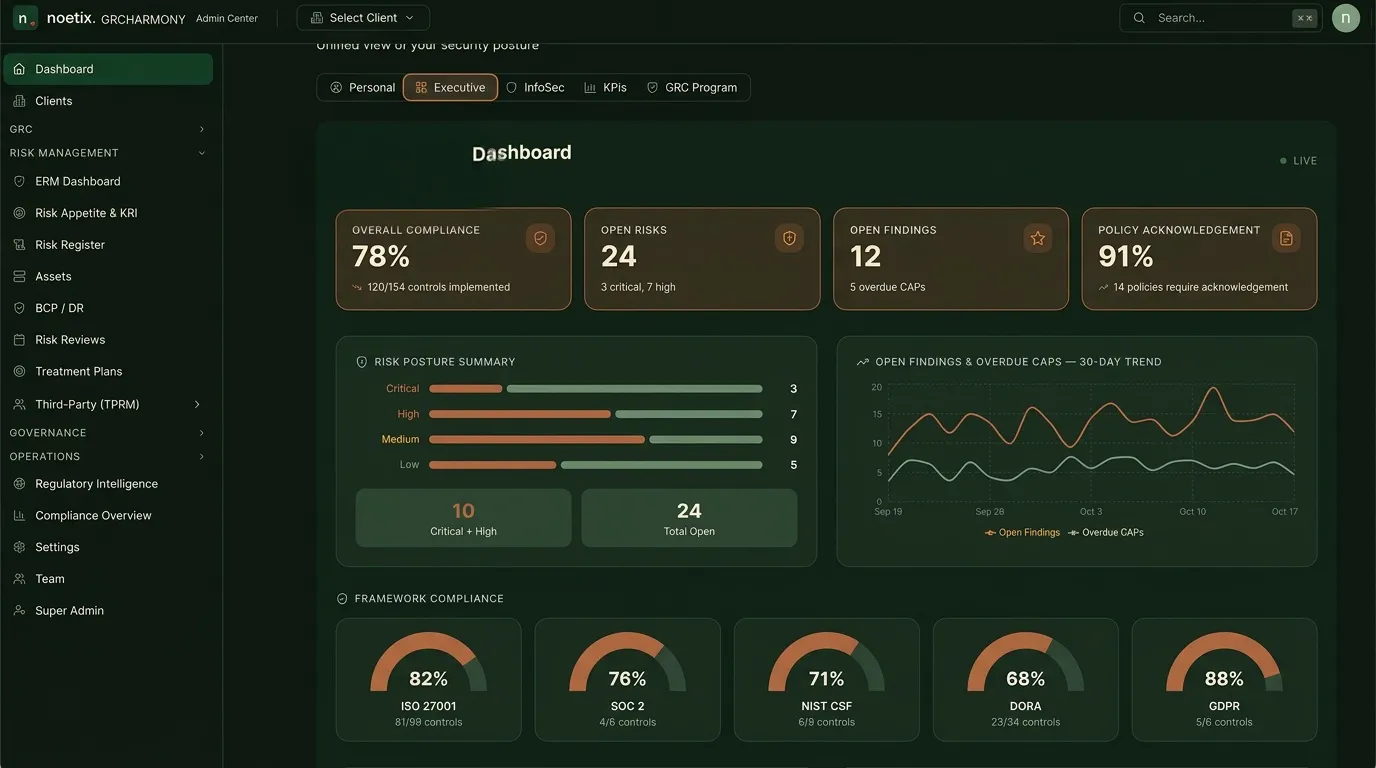
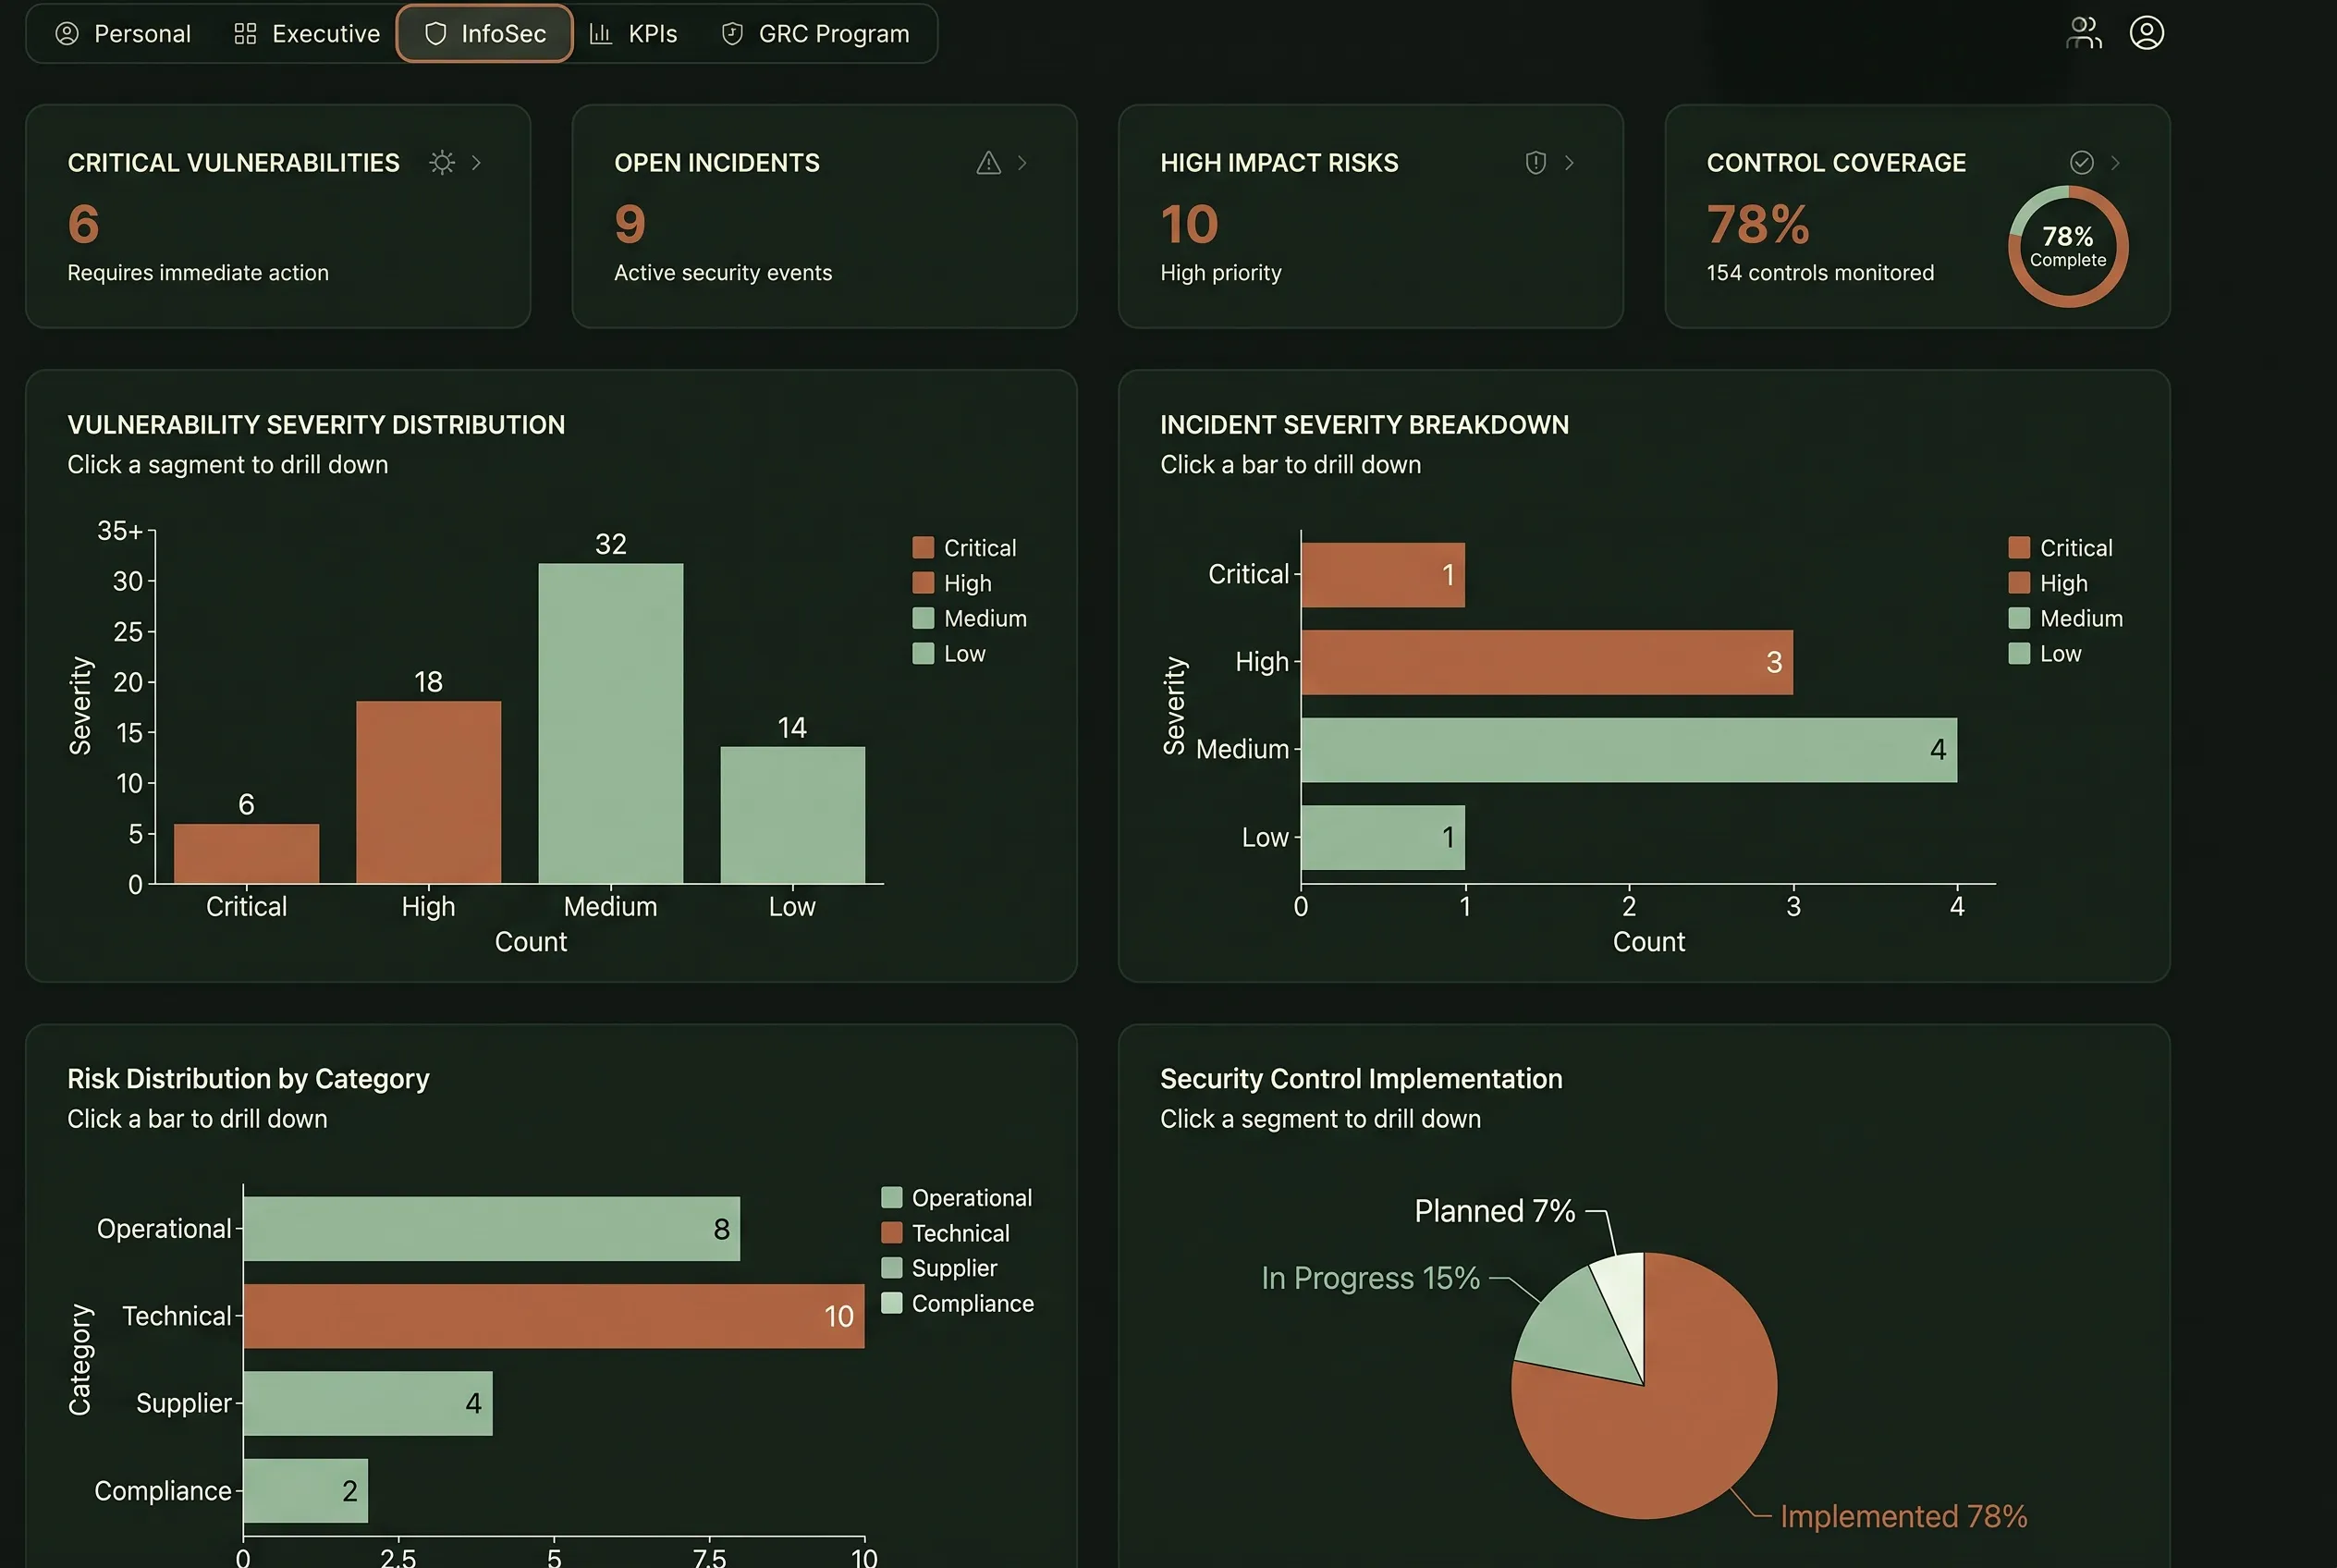
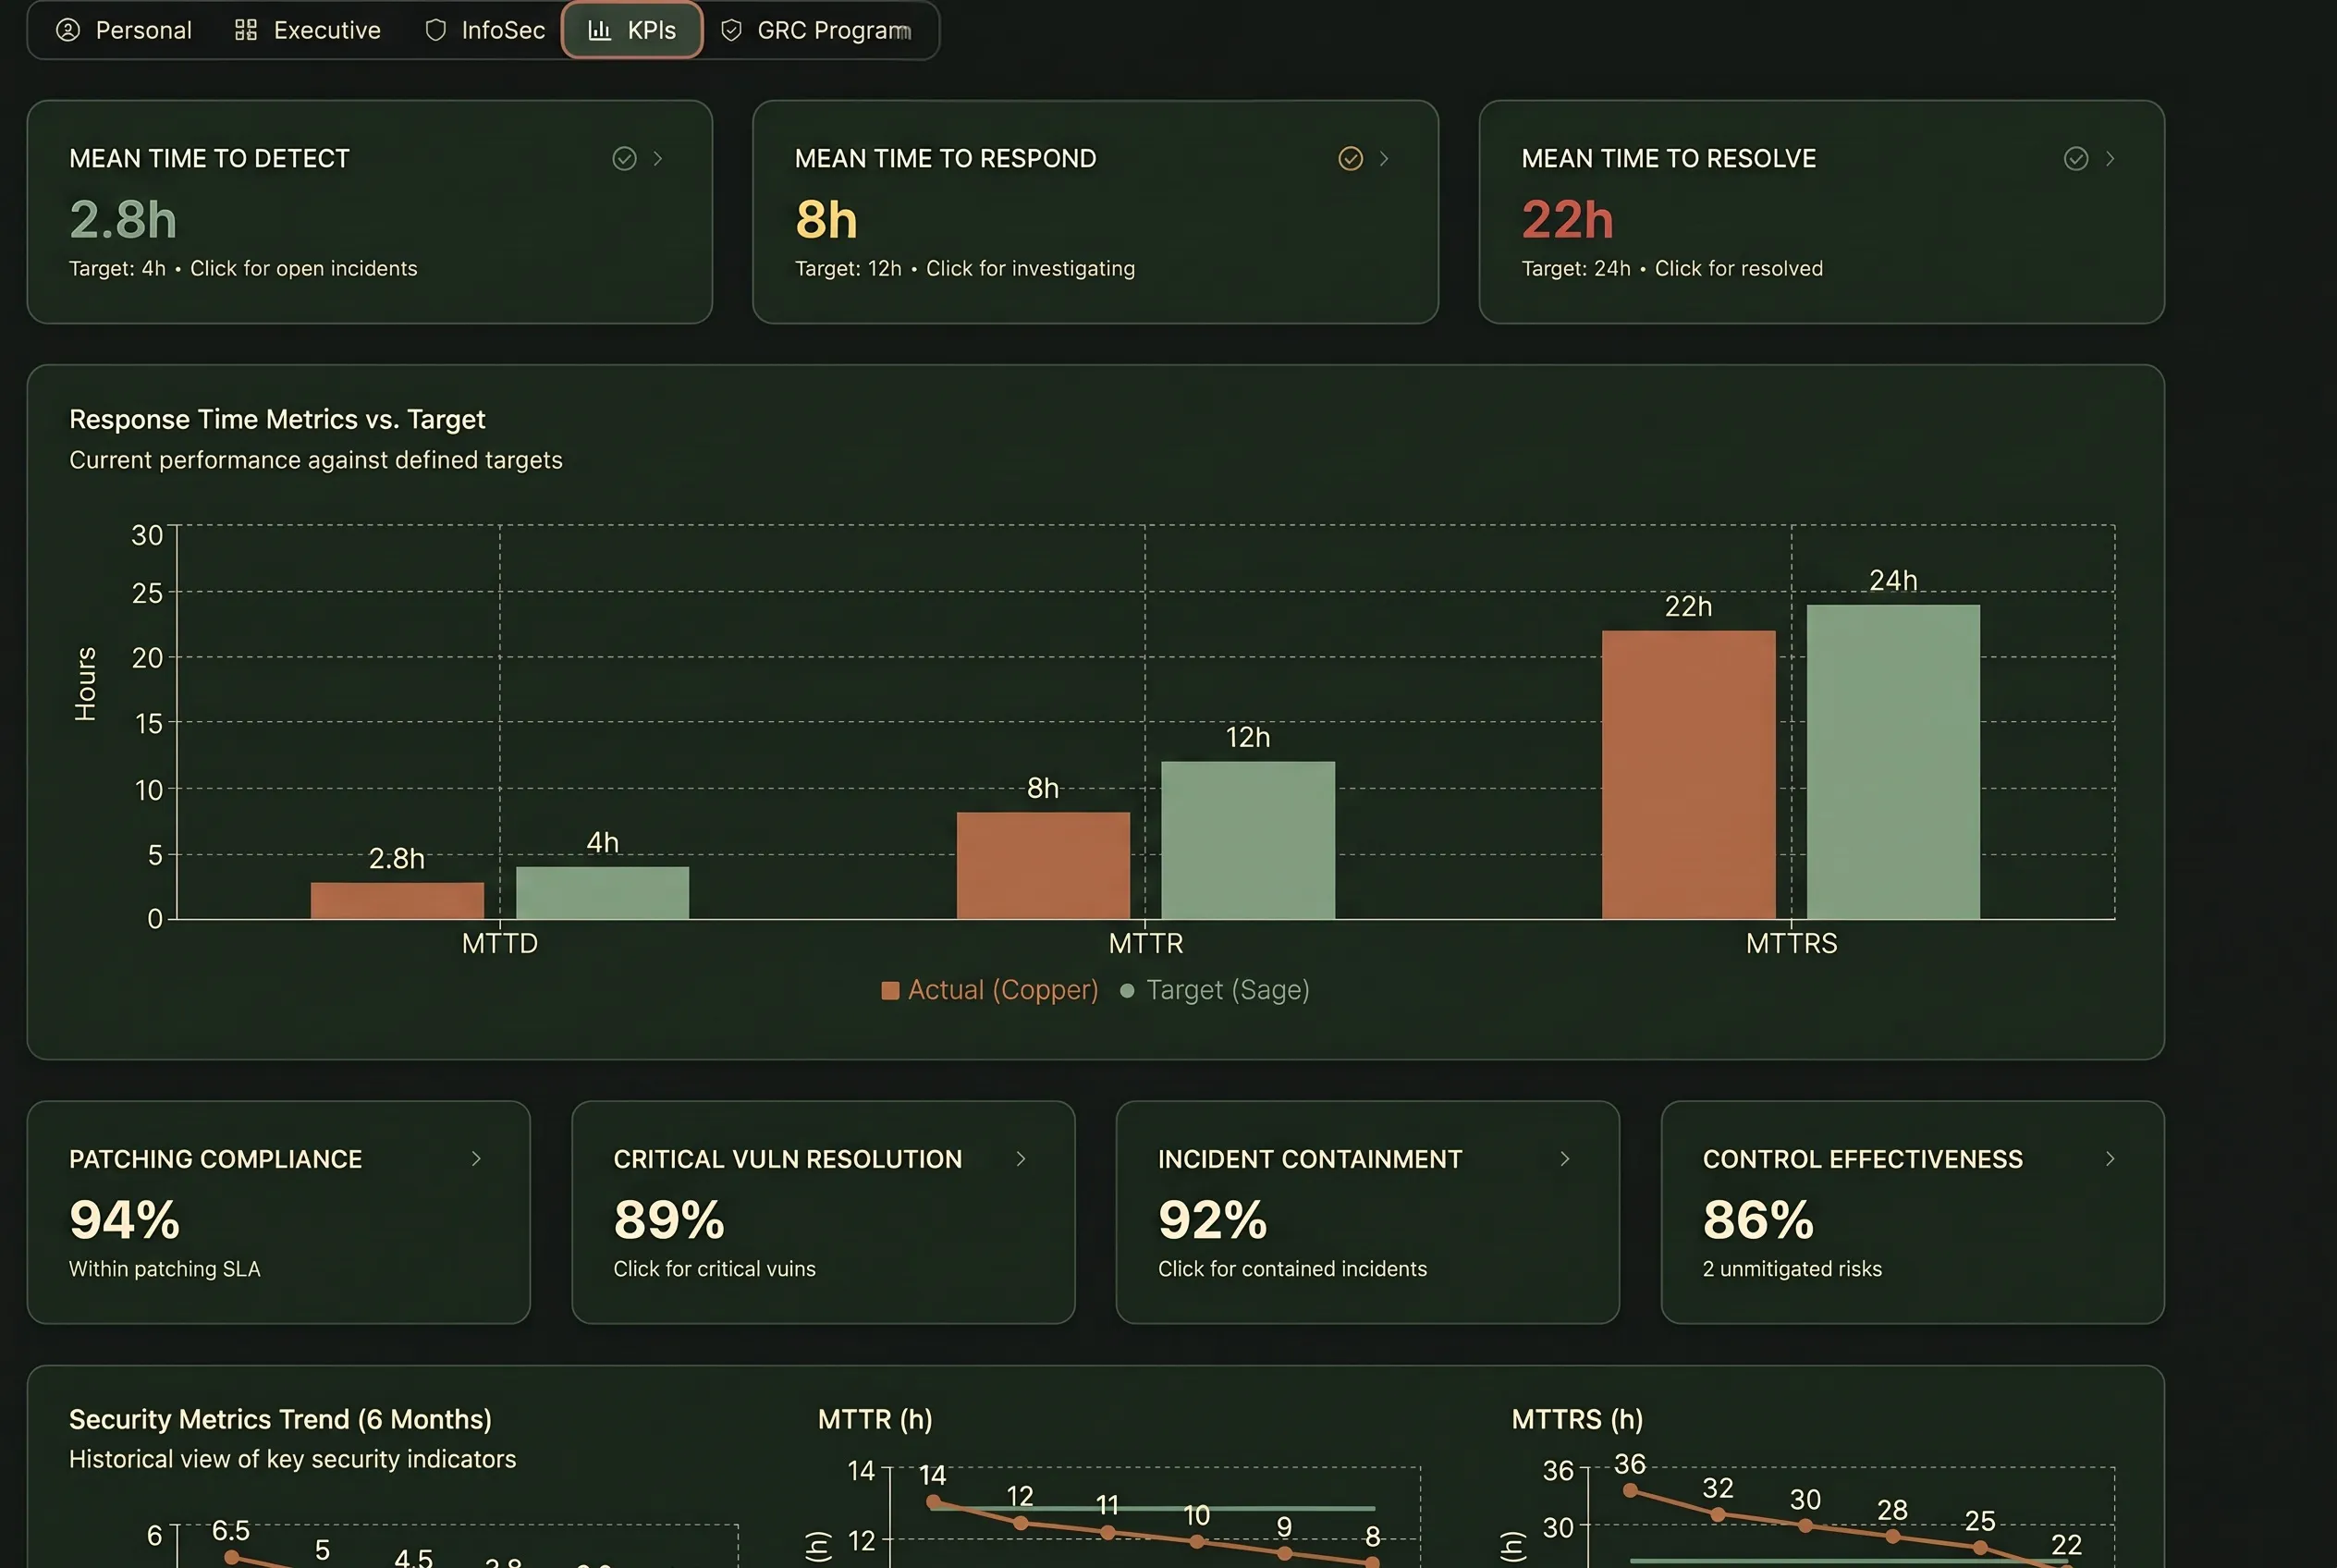
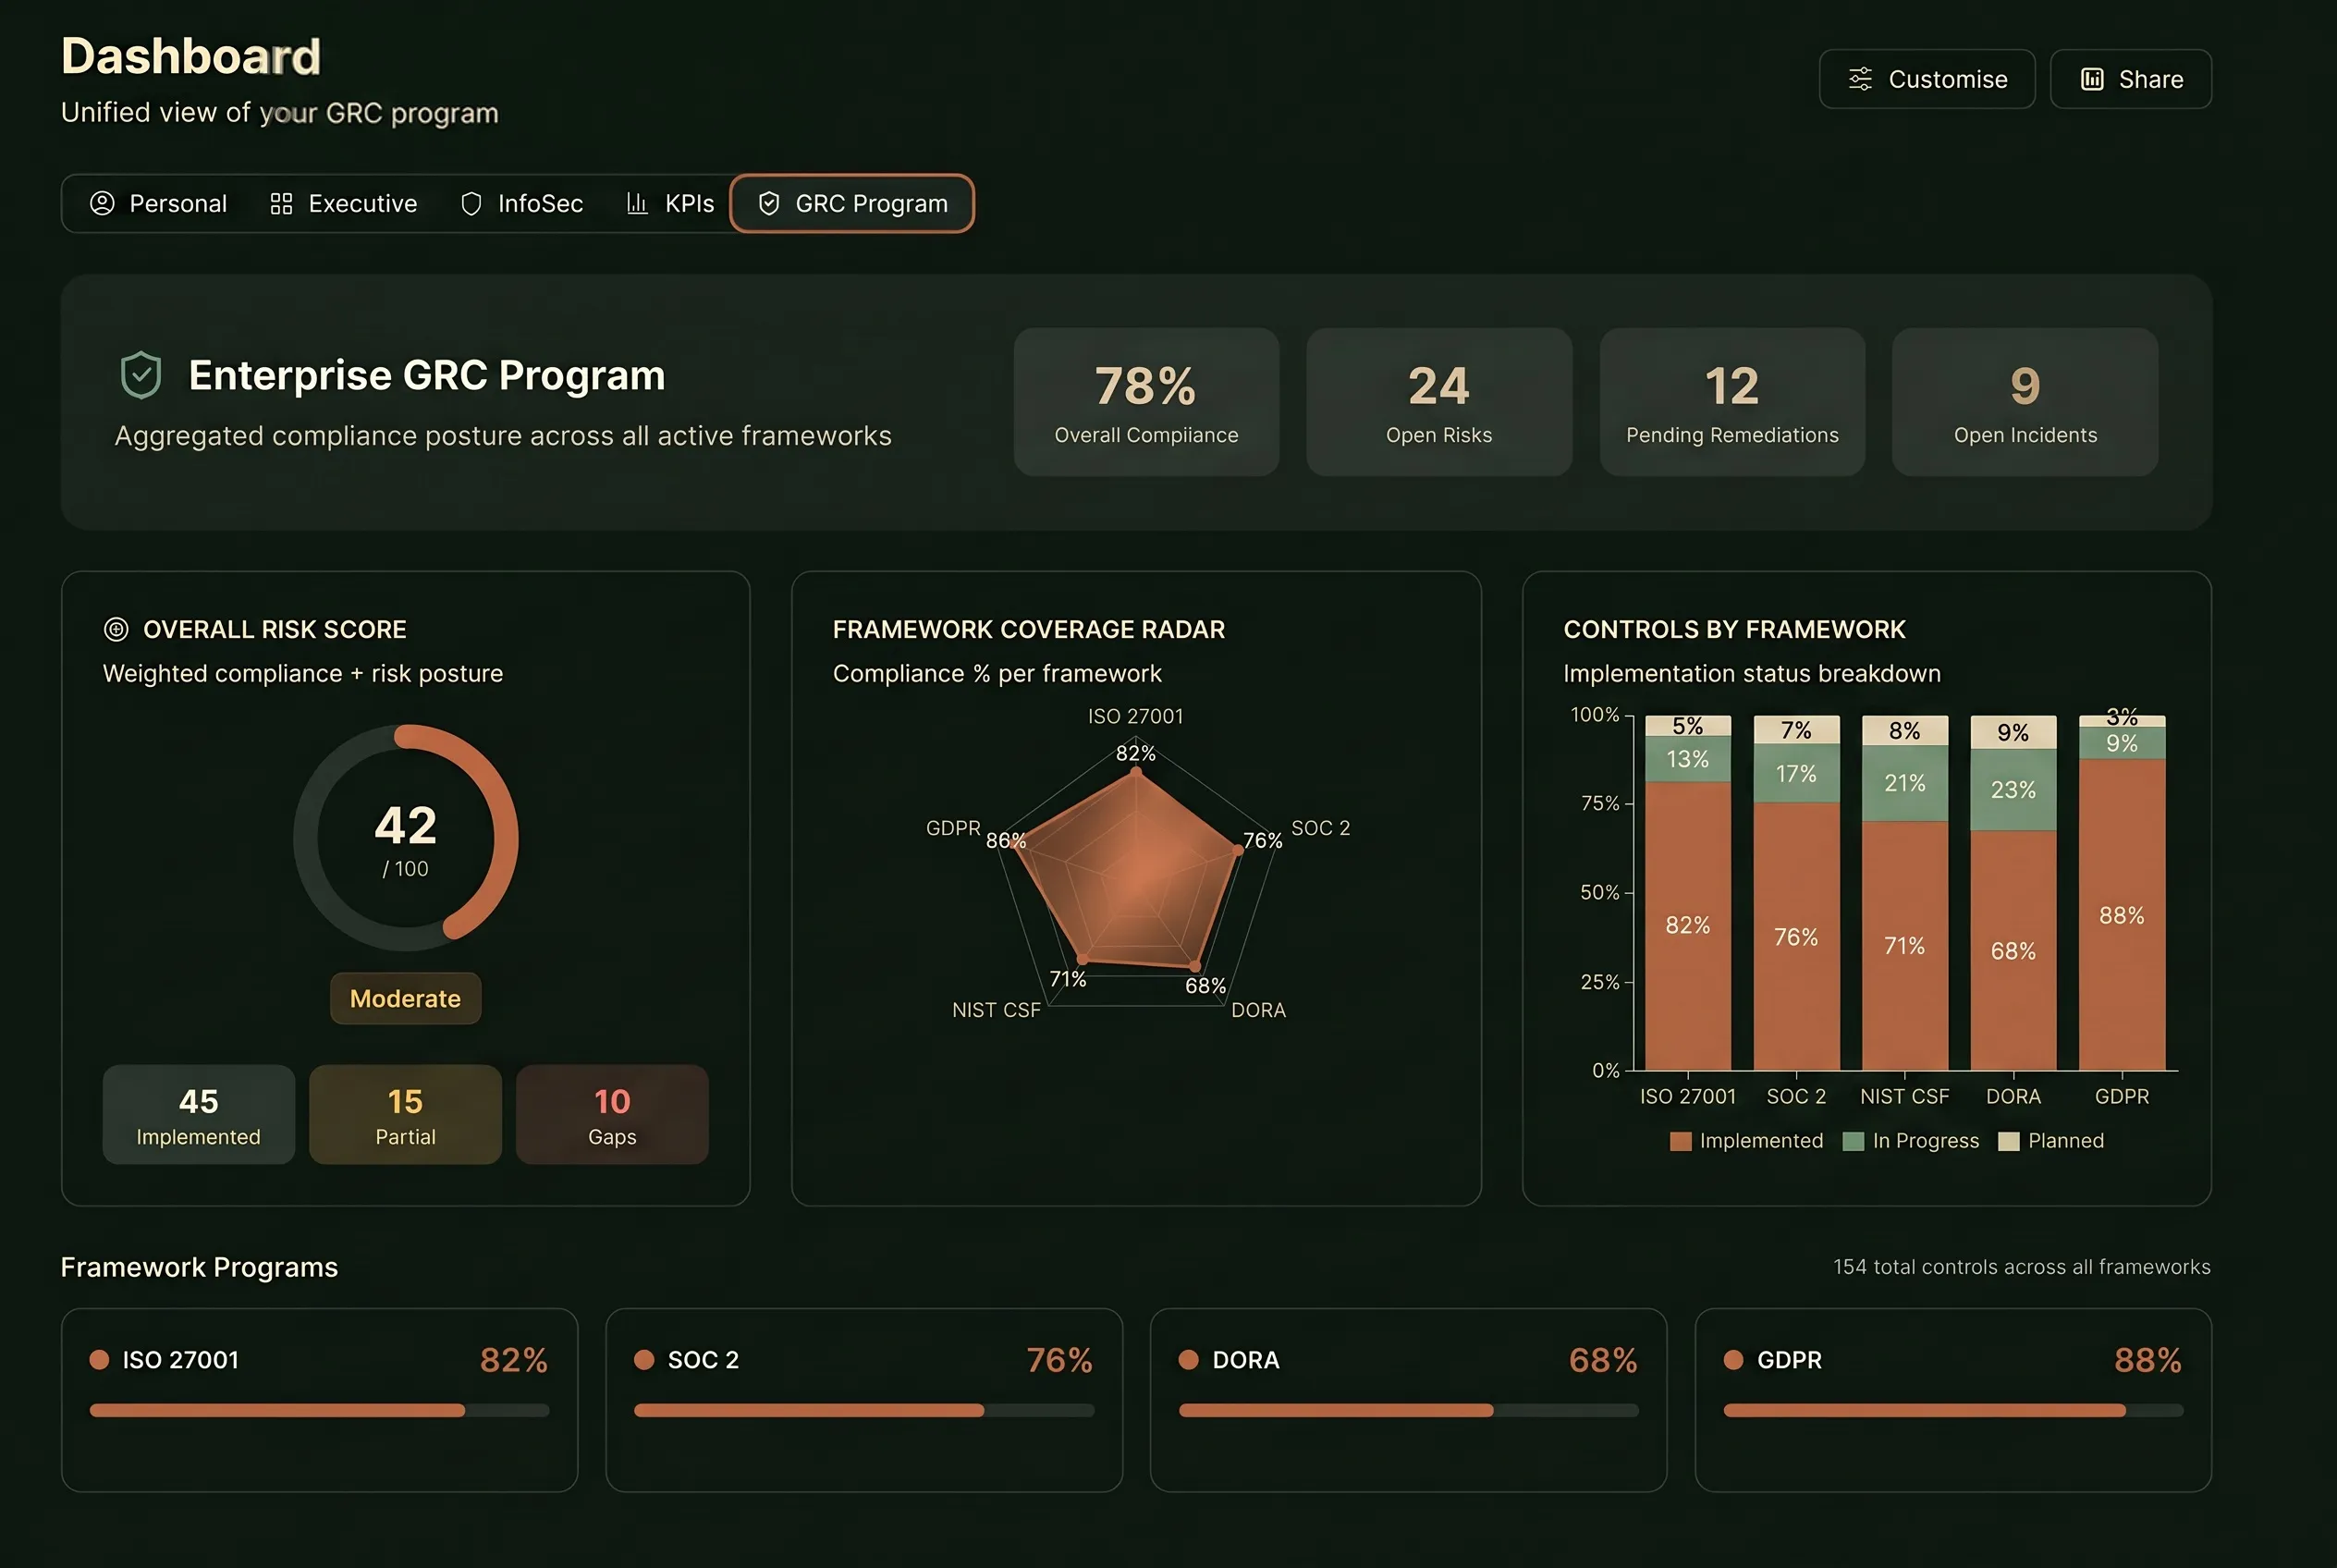
Product screens shown with illustrative data.
Let us discuss your risk or governance priorities
Across any or all of these service lines.